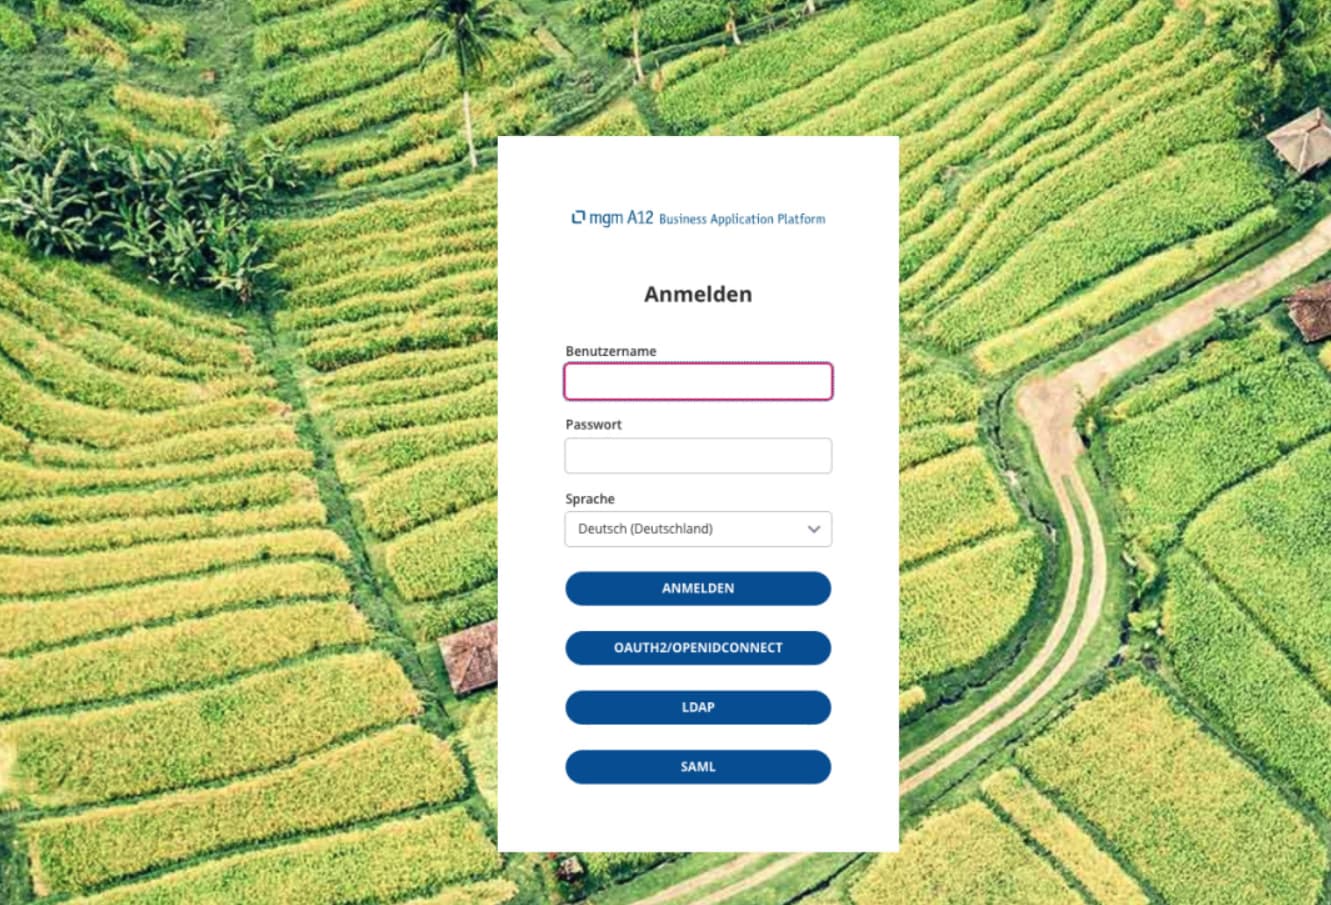
Hey,
we connected our A12 application with UAA to an OAuth2 IDP (Keycloak) and planning to give additional, custom information in the login-request (to communicate which login-types the IDP should display to the user to select from).
Does anybody know if something like this is possible and what is the easiest way to get it to work with UAA?
I imagined the login-request could be looking something like:
https://<idp-url>/realms/<realm>/protocol/openid-connect/auth?client_id=<...>&...&custom_parameter_1=value1&custom_parameter_2=value2
But other ideas are very welcome as we are currently investigating if something like this would be feasible.
Hi tkalkus,
If I understand you correctly, your final purpose is to support multiple authentication types at the same time, isn’t it?. If so, I suggest you to try the approach that Uaa is using with the dev-app example.
We make up a login page that contains all supported authentication types and users are able to determine which type they intend to proceed.
For example, if the user aims to use oauth2 protocol by hitting the Oauth2/OpenIdConnect button, the application will direct him to the IDP link which you also mentioned above. That link is used for and only for oauth2 authentication type, not for any others and might vary differently between IDP vendors. It’s the same mechanism with Saml follow that also leads the user to the corresponding IDP saml link. That’s why transmitting the custom parameters inside the IDP url, in my opinion, is not really an idea.
Hope this would help and please let me know if you have other concerns.
No, this isn’t what we want/can do sadly. We have this single external IDP that is provided by an external partner, which then provides the different login methods. We don’t have direct access to these login methods so the approach you posted does not work for us.
We are “just” looking for a way that is supported by UAA to send additional data in the request to tell our external IDP which of the login methods we want the user to use, so we can propose this to the external partner for future implementation.
We where able to figure some potential way to acchieve this (thanks @anh-fresh-forge for the support).
The external IDP (Keycloak) is providing its login options as a broker. These brokers can be pre-selected by using the query parameter kc_idp_hint=<brokerId>, see https://www.keycloak.org/docs/latest/server_admin/index.html#default_identity_provider
The oidc client used by UAA actually does provide the functionality to add extraQueryParams:
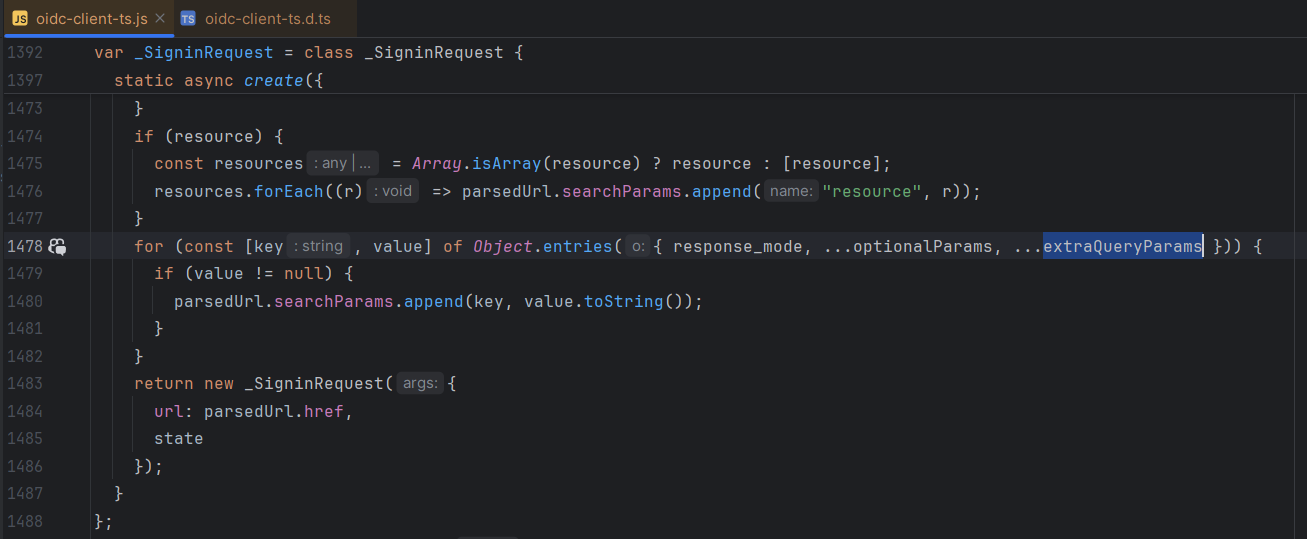
We’ll now need to figure out how we can configure this dynamically from our side. When we manage to do this I’ll update this thread with the final solution.
Hello @tim-steep-bit did you already figured out how to solve it on your side? And could you provide the solution?
The integration of the feature got postponed for now, so we didn’t continue with implementing this into a working state, sorry