Hi,
We need to switch our authentication from BundId (SAML) to a new Keycloak (which federates BundId and other IDPs) using OAuth2. From my understanding, the token we get contains only a few attributes like ID, firstname, and lastname. Other attributes (like address, email, etc.) must be requested by using the userinfo endpoint (see also Secure applications and services with OpenID Connect - Keycloak). Does UAA support this in any way (in the backend/dataservice), or do we need to implement this by ourselves? In any case, does someone have some example code on how this can be done in a secure way?
Thanks,
Guido
Hi Guido,
In backend side you can extract the user information from JWT.
        Authentication authentication = SecurityContextHolder.getContext().getAuthentication();
        Object token = Optional.ofNullable(authentication)
                .orElseThrow(() -> new IllegalStateException("No user in the security context"))
                .getCredentials();
        if (token instanceof Jwt jwt) {
            String email = jwt.getClaims().getOrDefault("email", "").toString();
        }
Hello @guido-quiet-root,
Please have a look at Principal Extension., in this case, the project has to config mapping of those Other attributes (like address, email, etc.) from keycloak to UAA principal property first, into new principal lets say ProjectExtendedPrincipal (that has properties such as address, phone number, etc). Then, like @Phuoc suggestion, we can get the extended principal with something like
...
public static ProjectExtendedPrincipal currentUser() {
		var cur = SecurityContextHolder.getContext().getAuthentication().getPrincipal();
		if (cur instanceof ProjectExtendedPrincipal user) {
			return user;
		}
...
The implementation details could be complicated; please consider referring to UAA training resources.
Thank you
Hi,
thanks for the response. Unfortunately, the other attributes (emails, etc) are not part of the token, so they cannot be extracted that way. From my understanding, we need to use the userinfo endpoint to get those. So again my question is, does UAA call this endpoint by itself, or do we need to do that ourselves?
Thanks,
Guido
hi @guido-quiet-root
The UserInfo get called in Front-end via uaa-authentication-client so yes it’s supported out of the box (the default value fetch user-info is true).
The similar implementation is done in uaa-rest-client. So using uaa-rest-client with configurations you should have user-info call out of the box.
UPDATED: After verifying, the user-info calling is not called out of the box in uaa-rest-client therefore you have few options:
- Create requirement so UAA team can implement it for you.
- Put the information in the token so that it can be loaded in the token.
- Use user-info feature in javascript/front-end part.
Cheers,
Tuan Do
Hi @guido-quiet-root
I think your question regarding to how server can get these firstname or last name from the access_token (jwt string) if correct then refer to below example:
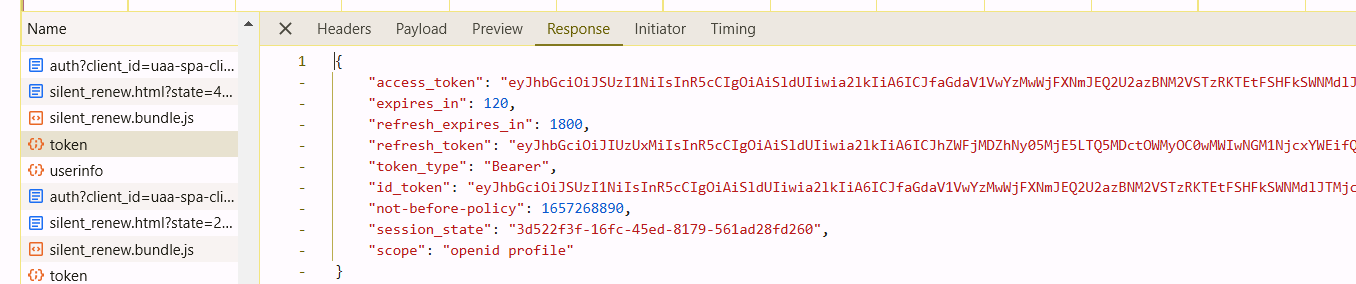
The first one is response of /token endpoint [From Keyloak]
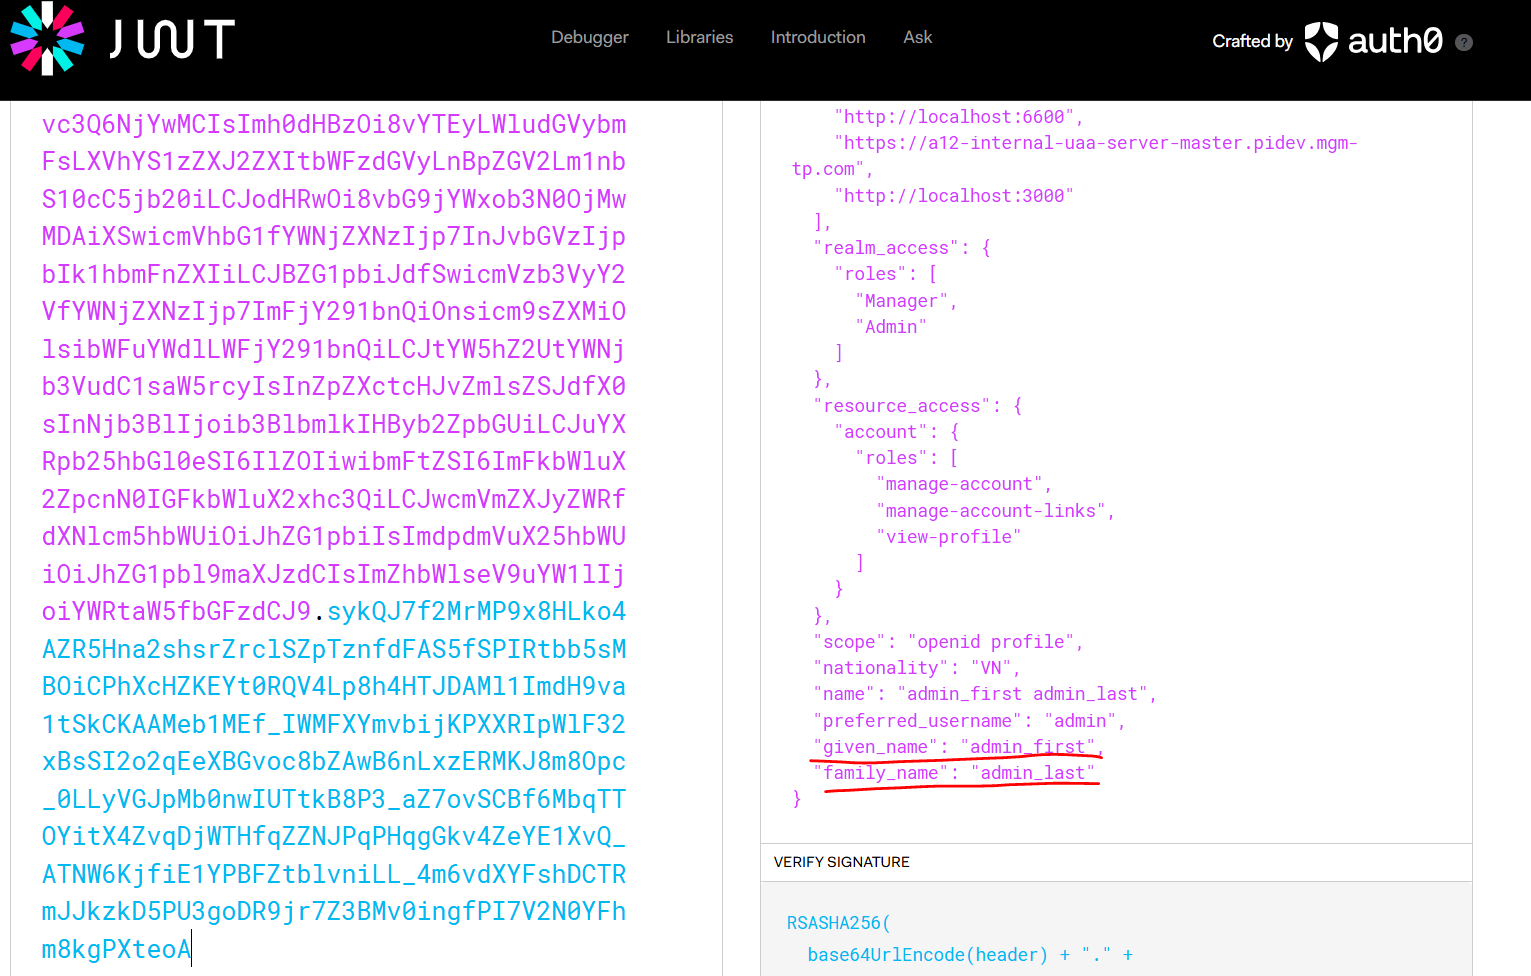
and below is what we have inside the jwt access_token string
You can control what can display inside this token from IDP configuration (e,g viva client scope of keycloak)
From server by using UAA you can extract these infomration from the access_token to build a principal.
Thanks
Hello @guido-quiet-root , I am a member of the Discourse team. I can see that there was a new response to your question on the Topic of the discussion. Do you find it helpful or should the question remain open?
Thanks ahead for your feedback and have a nice rest of the day!