We have an A12 application running in a Kubernetes Cluster. Authentication should be done via Keycloak (also running in the cluster).
The application can be reached through two different domains (either one or the other, depending of the network), let’s call them xxx.A.domain and xxx.B.domain:
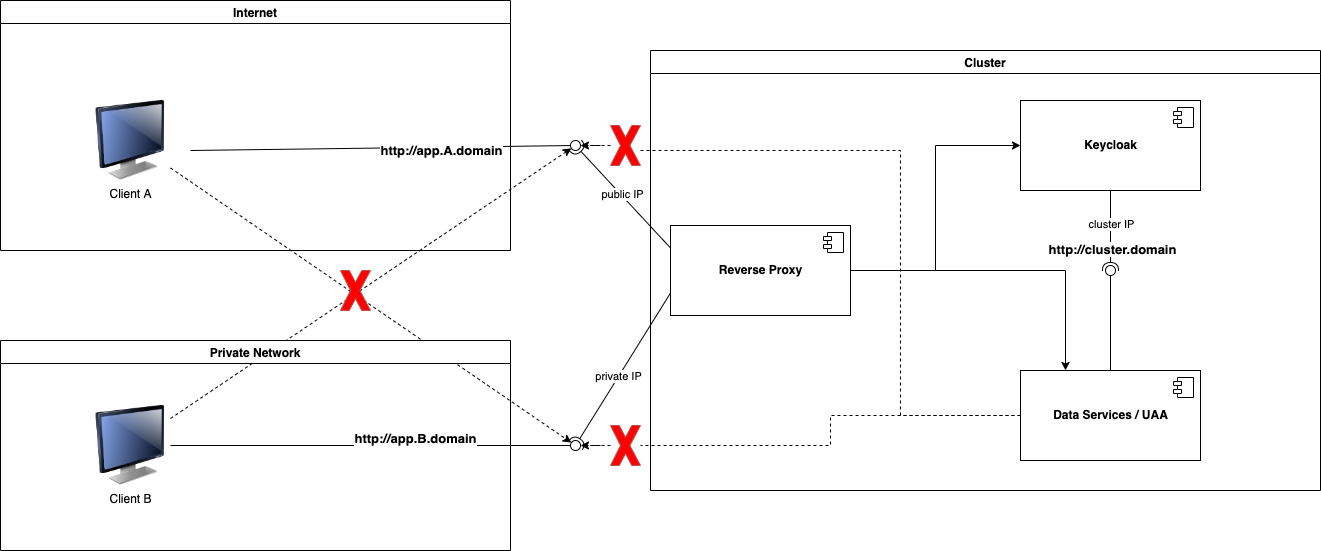
On server side, the following configuration is used for UAA:
mgmtp.a12.uaa.authentication.oauth2.jwt-issuer-uris=http://app.A.domain,http://app.B.domain
This does not work, because UAA is trying to load configuration from both URLs, but it can’t.
When I use the following configuration:
spring.security.oauth2.resourceserver.jwt.jwk-set-uri=http://cluster.domain
spring.security.oauth2.resourceserver.jwt.issuer-uri=http://app.A.domain
It seems to be working for one URL. Using the other one of course does not work, because UAA/Spring Security fails to validate a token with an Issuer URI that it does not know.
Is there some configuration option, that does the same like my second option, but for two URLs?
As soon as I wrote that post, I discovered that I can use following configuration:
mgmtp.a12.uaa.authentication.oauth2.jwt-set-uris[0].jwt-set-uri=http://cluster.domain
mgmtp.a12.uaa.authentication.oauth2.jwt-set-uris[0].algorithm=RS256
This seems to actually work with tokens issued from both URLs. But the documentation states, that in this case, the Issuer will not be validated. How much of a security issue is that?
jwk-set-uri is validate for timestamp only if you want to validate for Issuer then please uses jwt-issuer-uris
Below is an example:
mgmtp.a12.uaa.authentication.oauth2.jwt-issuer-uris=http://localhost:9090/realms/UAARealm,http://localhost:9090/realms/UAARealmII
For more detail, you can check on the getA12Document or use our internal link <INTERNAL_LINK>
Thanks,
Yes, but i can’t use jwt-issuer-uris
When I use jwt-issuer-uris, UAA tries to make an http request to those URIs, but it can’t do that for strange networking reasons. UAA can only contact Keycloak by its cluster internal URL. But I cannot use that as Issuer URI, because the tokens are issued by the other two URIs…
I am not sure about the networking problem you are facing but I think in the above configuration you made is incorrect (it should be keycloak uri). Below is what we push in our example. Can you check it?
spring.security.oauth2.resourceserver.jwt.jwk-set-uri=http://localhost:9090/realms/UAARealm/protocol/openid-connect/certs
spring.security.oauth2.resourceserver.jwt.issuer-uri=http://localhost:9090/realms/UAARealm
Only use mgmtp.a12.uaa.authentication.oauth2.jwt-issuer-uris (UAA base configuration) in case you have multiple realms for different applications otherwise you can use the Spring base configuration.
Our Keycloak Realm can be reached by two URLs:
http://app.A.domain/…
http://app.B.domain/…
UAA cannot reach any of these URls directly, but has to use http://cluster.domain, to contact Keycloak.
The issuer URI inside the tokens from Keycloak can be either http://app.A.domain/… or http://app.B.domain/…, depending on the route the client took. So UAA needs to be able to validate both Issuers.
If I use
spring.security.oauth2.resourceserver.jwt.issuer-uri
I can only pass one of those URLs.
If I use
mgmtp.a12.uaa.authentication.oauth2.jwt-issuer-uris
I can pass both URLs, but in that case UAA tries to download the configuration for both URLs, which failes because of firewalls. It can only download configuration and certificates from http://cluster.domain
But nevermind, I will use
mgmtp.a12.uaa.authentication.oauth2.jwt-set-uris[0].jwt-set-uri
with the internal cluster URL for now, because this seems to work.
Hello,
have you tried the:
spring.security.oauth2.resourceserver.jwt.jwk-set-uri
Yes. This works well for either one of the URIs, but since I cannot configure both here (afaik), it does not work for the other one.