Hi guys,
I’m using A12 Helm chart version 5.1.1, of which the Keycloak version is 21.0.2 (and it is working).
And I’m trying to boot the version of Keycloak to 23.0.4 (due to vulnerabilities of the 21.0.2.)
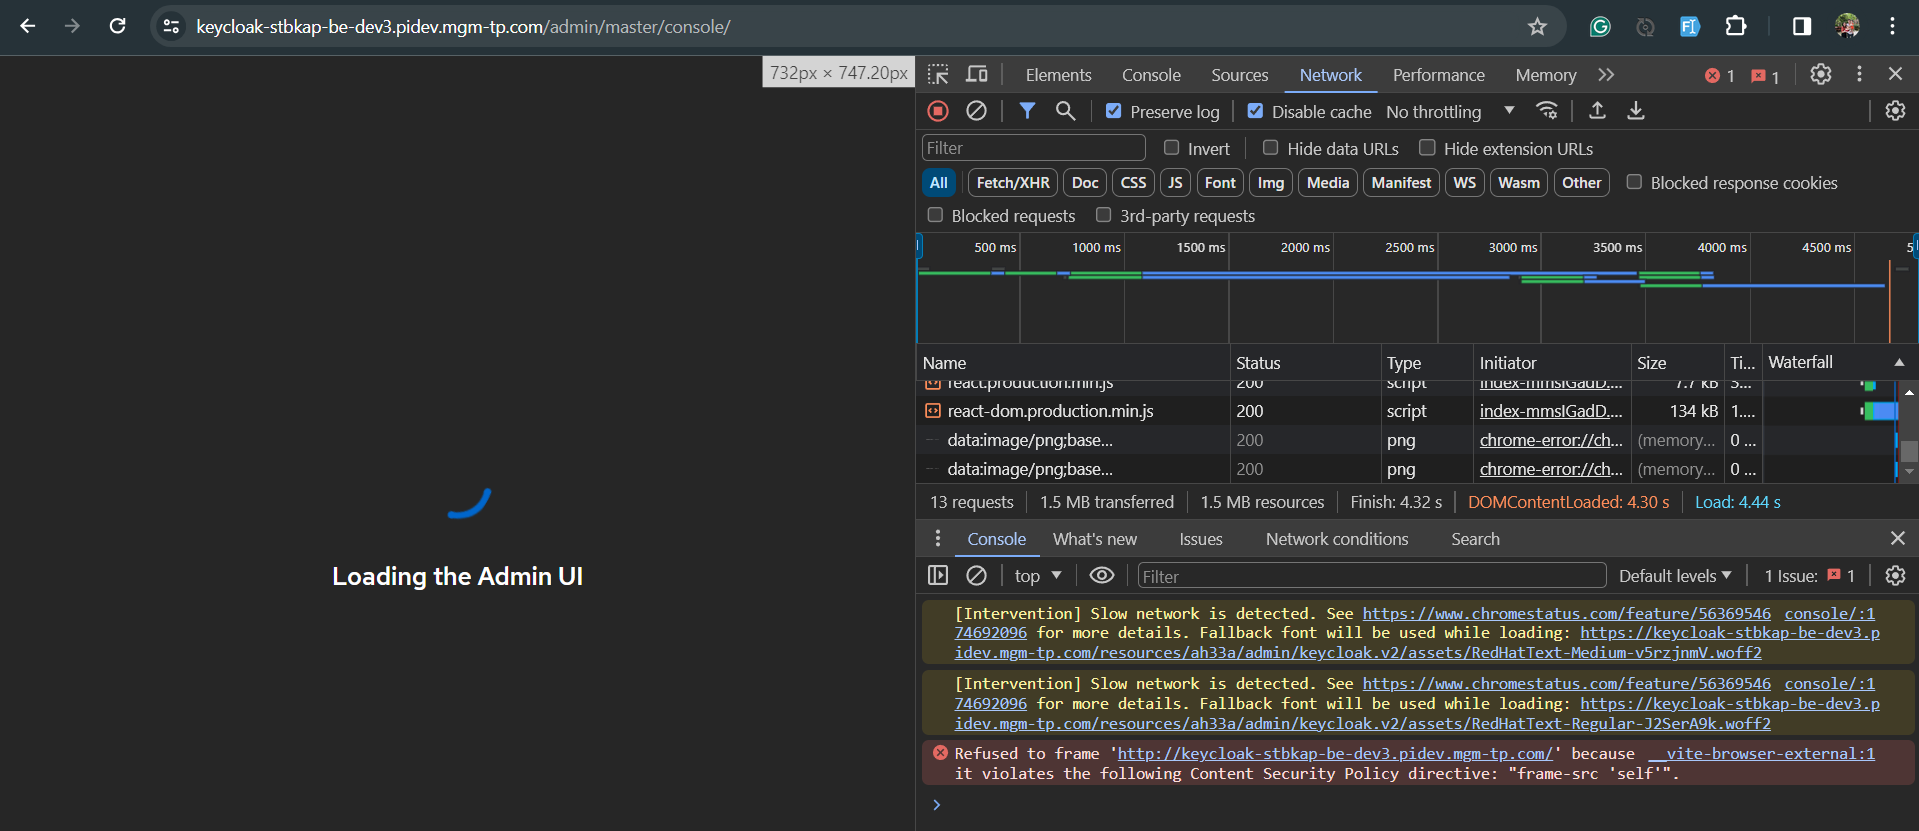
But if I try to access the Admin Console (from the Keycloak homepage) via https, the log-in UI cannot be loaded due to this error.
Refused to frame '<INTERNAL_LINK> because it violates the following Content Security Policy directive: "frame-src 'self'".
The iframe error is, apparently, because I access Keycloak homepage using
https, but the iframe tries to load a
http link, which violates one of Keycloak’s default Content Security Policies
"frame-src 'self'".
``
(Using
http, the Admin Console can be accessed normally.)
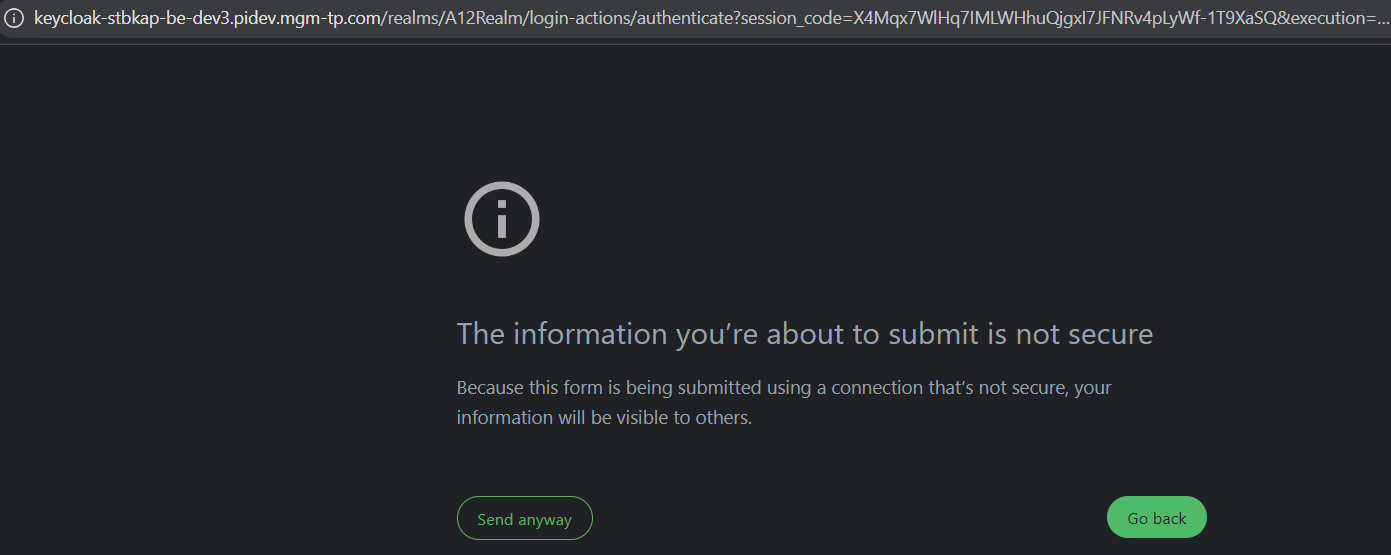
In addition, when I access our app, I get redirected to the login screen but after I enter username + password and click login, this warning screen is shown.
If I click
Send anyway, then I get a
502 Bad Gateway.
Have you guys encountered this error before? Is there any quick way to solve this problem?
@guido-quiet-root @tim-steep-bit @felix-warm-oat
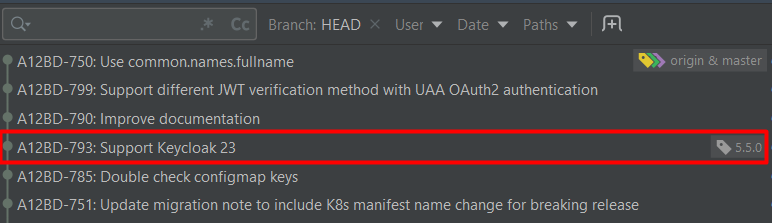
There is a new version of the Helm chart 5.5.0, which seems to be for supporting Keycloak 23. I have not tried this out yet. I’d rather not update the chart version at the moment, though, as it could be risky and we are time-constrained.
Changing Content Security Pocily frame-src to include "<INTERNAL_LINK> will lead to this error when trying to access log-in page for Admin Console:
Mixed Content: The page at '<INTERNAL_LINK> was loaded over HTTPS, but requested an insecure frame '<INTERNAL_LINK> This request has been blocked; the content must be served over HTTPS.
Also, I’m not sure if this is secure even if it works.
Configure proxy: edge seems to solve the problem.
See: Using a reverse proxy - Keycloak
Hi @bao-rocky-dune,
as your comment changing from proxy: passthrough to proxy: edge can solve the problem. Besides, let me explain the issue.
The reported problem relates to your deployment on a cluster which supports TLS connection with a wild card SSL certificate. So the TLS connection will be terminated at the NGINX ingress and the connection to the Keycloak from the ingress will communicate via http protocol. That means your Keycloak is running with HTTP mode and behind a reverse proxy. Following the proxy mode section in Using a reverse proxy - Keycloak, we can use the proxy: edge in this case. However, please keep your eye on the security perspective in this section. It depends on your project security policy, you can change to a securer option when you go with production.
Additionally, it’s not recommended to update the CSP to allow HTTP protocol. At some point when you deploy to production with TLS enforcement, and you can only access to your application via HTTPS. Then the modification will become redundant and need to be removed.